Governance & hygiene · Storage Hygiene Scorecard
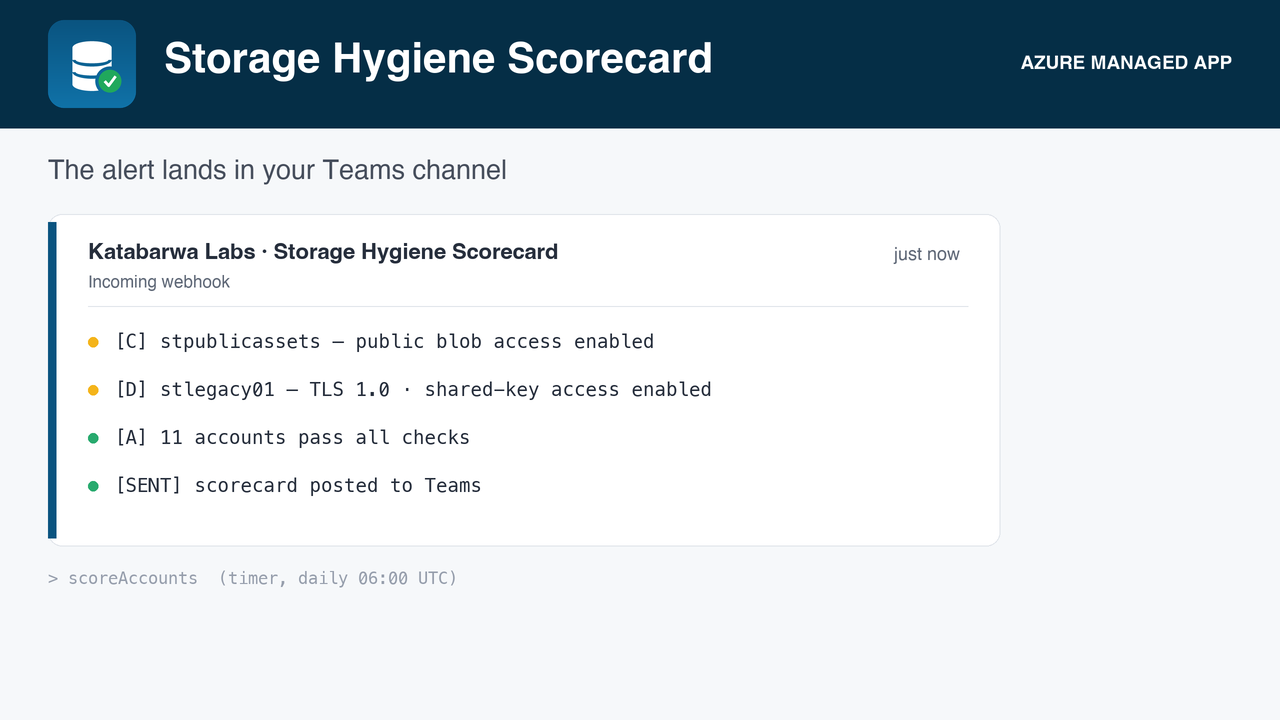
Anonymous blob access, shared-key auth, TLS floor, SAS policy, network default action: each account scored, the gaps named, the systemic ones ranked.
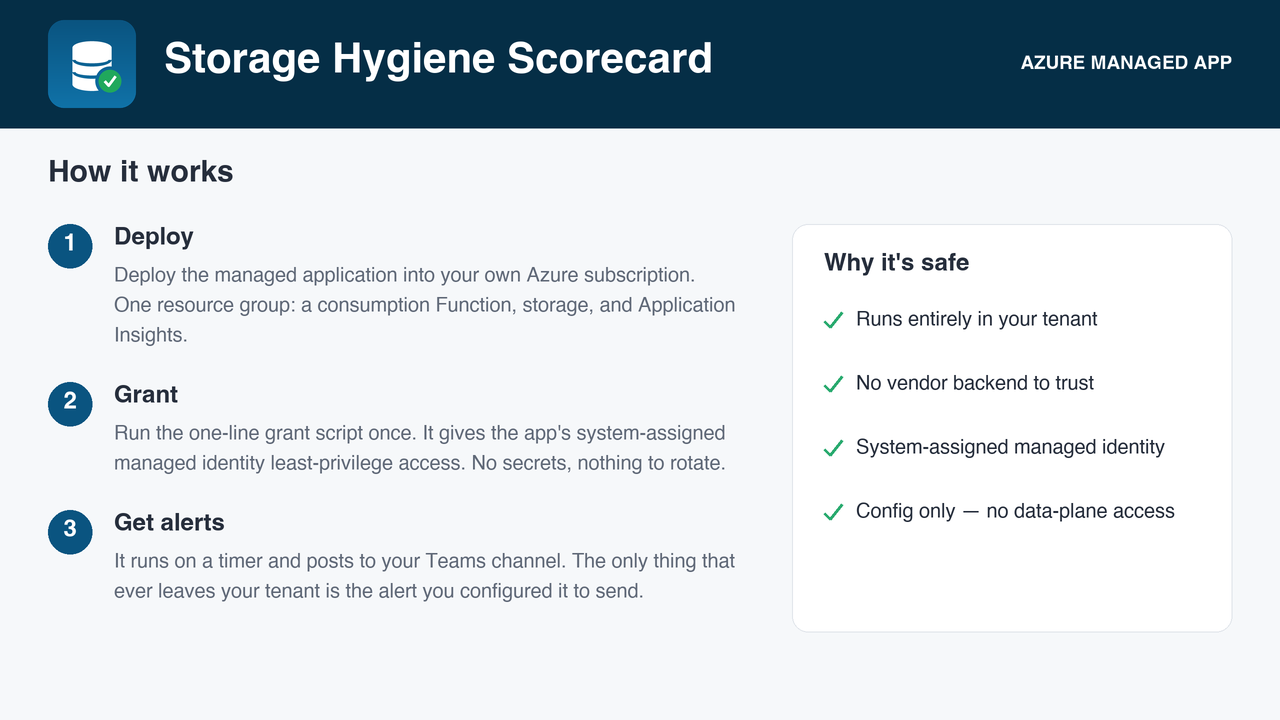
Deploys as a managed application in your own subscription. No vendor backend, no data egress. Flat monthly fee, billed by Microsoft.
One storage account with anonymous blob access left on is a breach. Across dozens of accounts created by different teams over years, nobody has the recurring view. The portal shows one account at a time and the checks are spread across five blades.
A serverless function on a schedule, with a system-assigned managed identity, deployed into your subscription by the Azure Marketplace. Roles are granted by you after deployment with the one-line script in the package, so nothing runs until you say so. Every role it asks for, and why:
| Reader | read storage account configuration |
Alerts go to the Teams webhook you configure. Nothing is sent anywhere else.
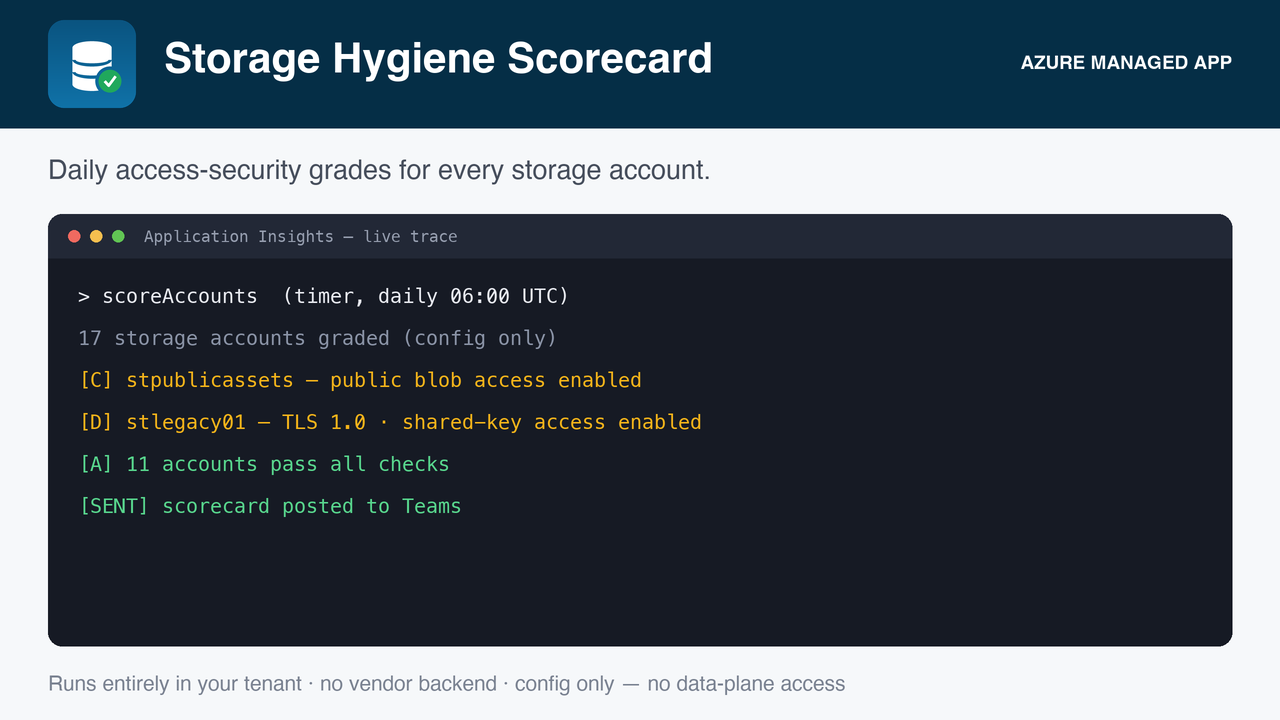
No. The function runs in your subscription and writes only to your configured alert destination. Katabarwa Labs operates no backend and receives nothing.
A flat monthly fee on your Azure bill through the Marketplace, plus the small consumption cost of the function itself. No per-resource or per-user pricing.
Delete the managed application from the Azure portal. Its resource group and identity go with it, and any role you granted can be removed the same way.
support@llmgraph.ai, or the support page.
Anonymous blob access, shared-key auth, TLS floor, SAS policy, network default action: each account scored, the gaps named, the systemic ones ranked.
Deploy from the Azure Marketplace