Jira · Compliance Log Vault
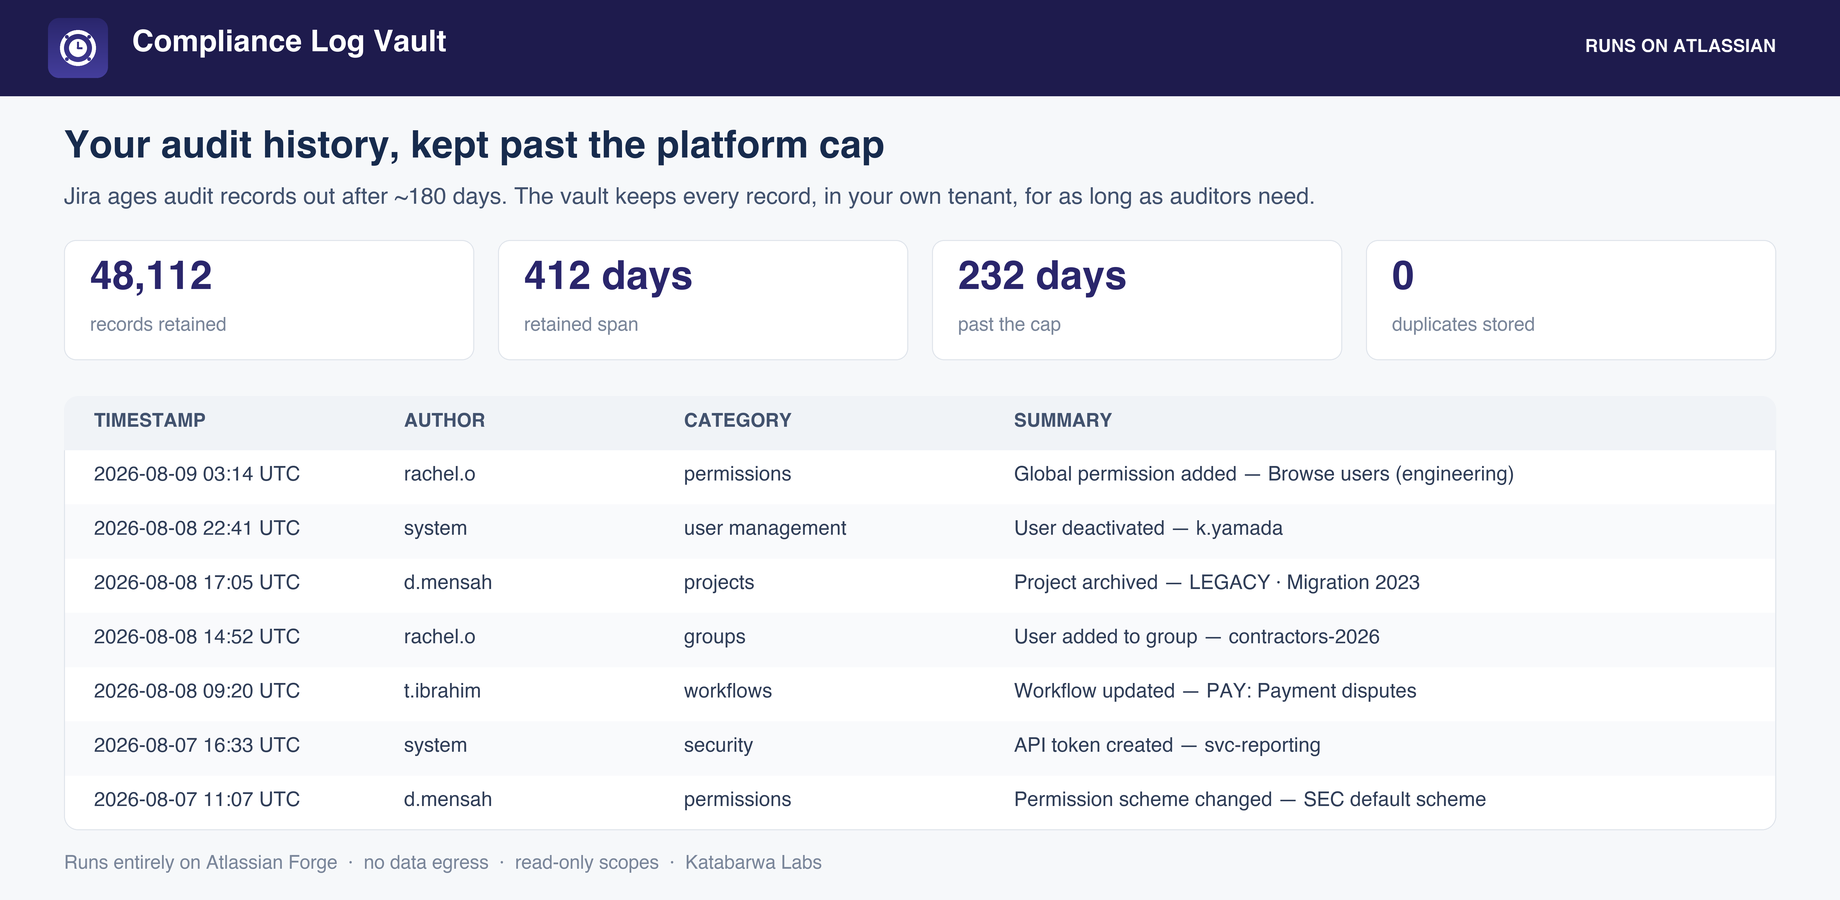
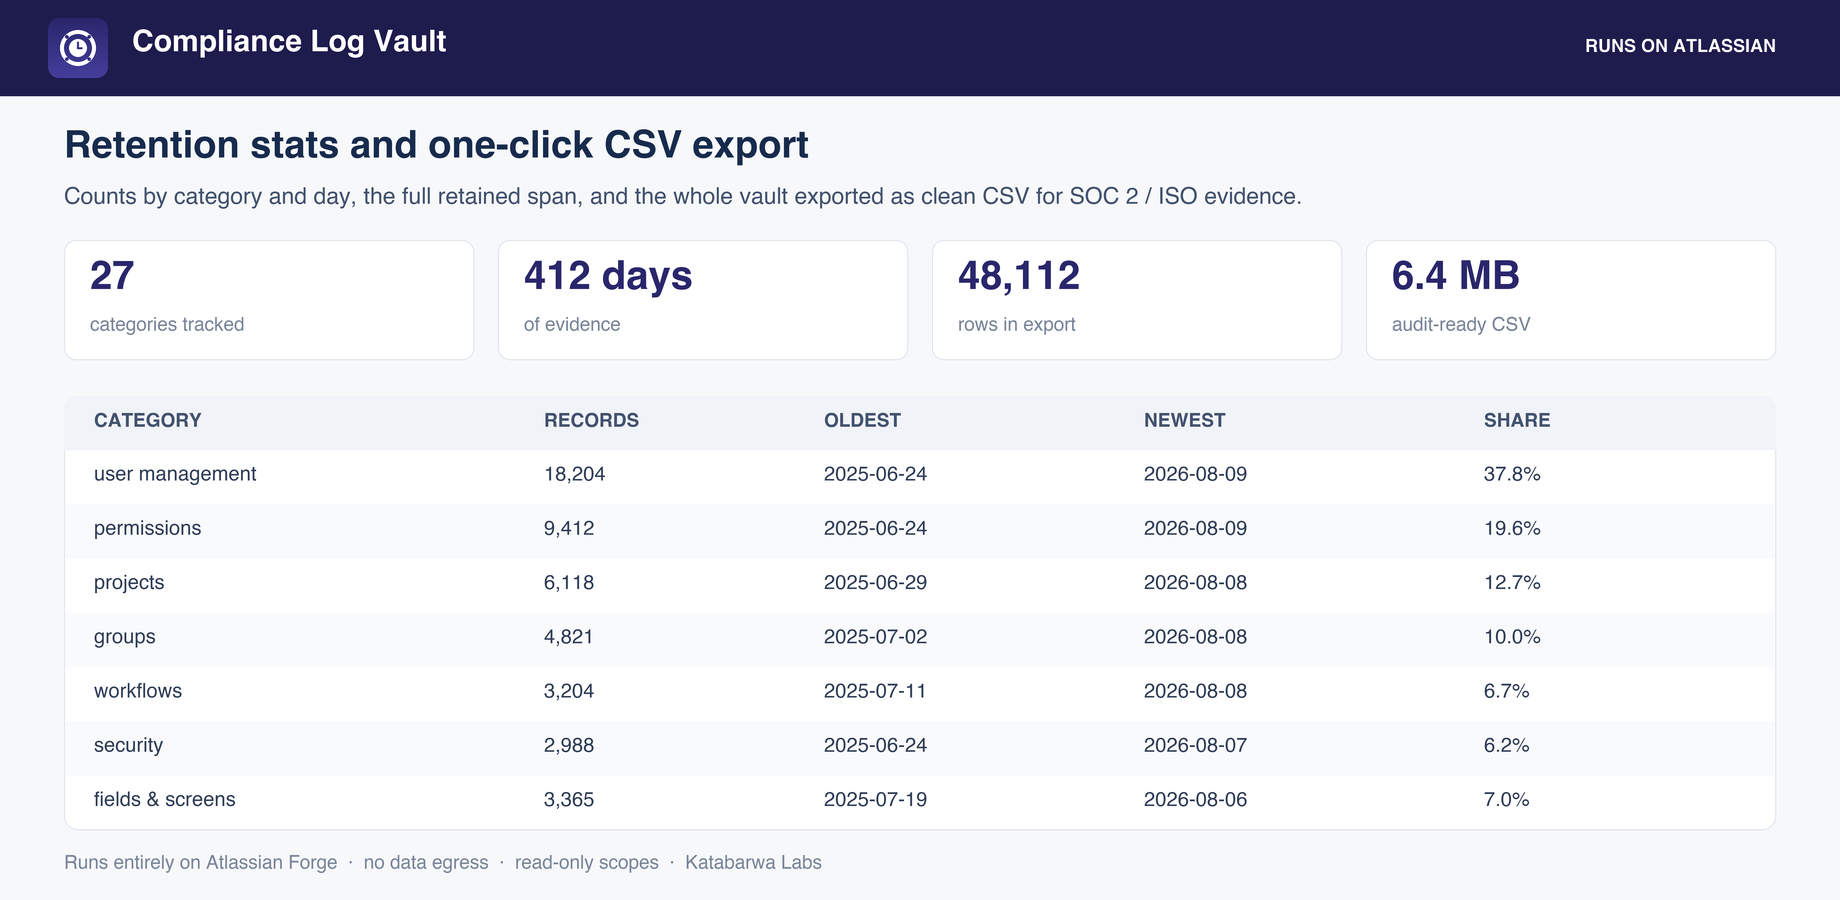
Retain Jira audit records long-term and export SOC 2 and ISO evidence. Runs entirely on Atlassian.
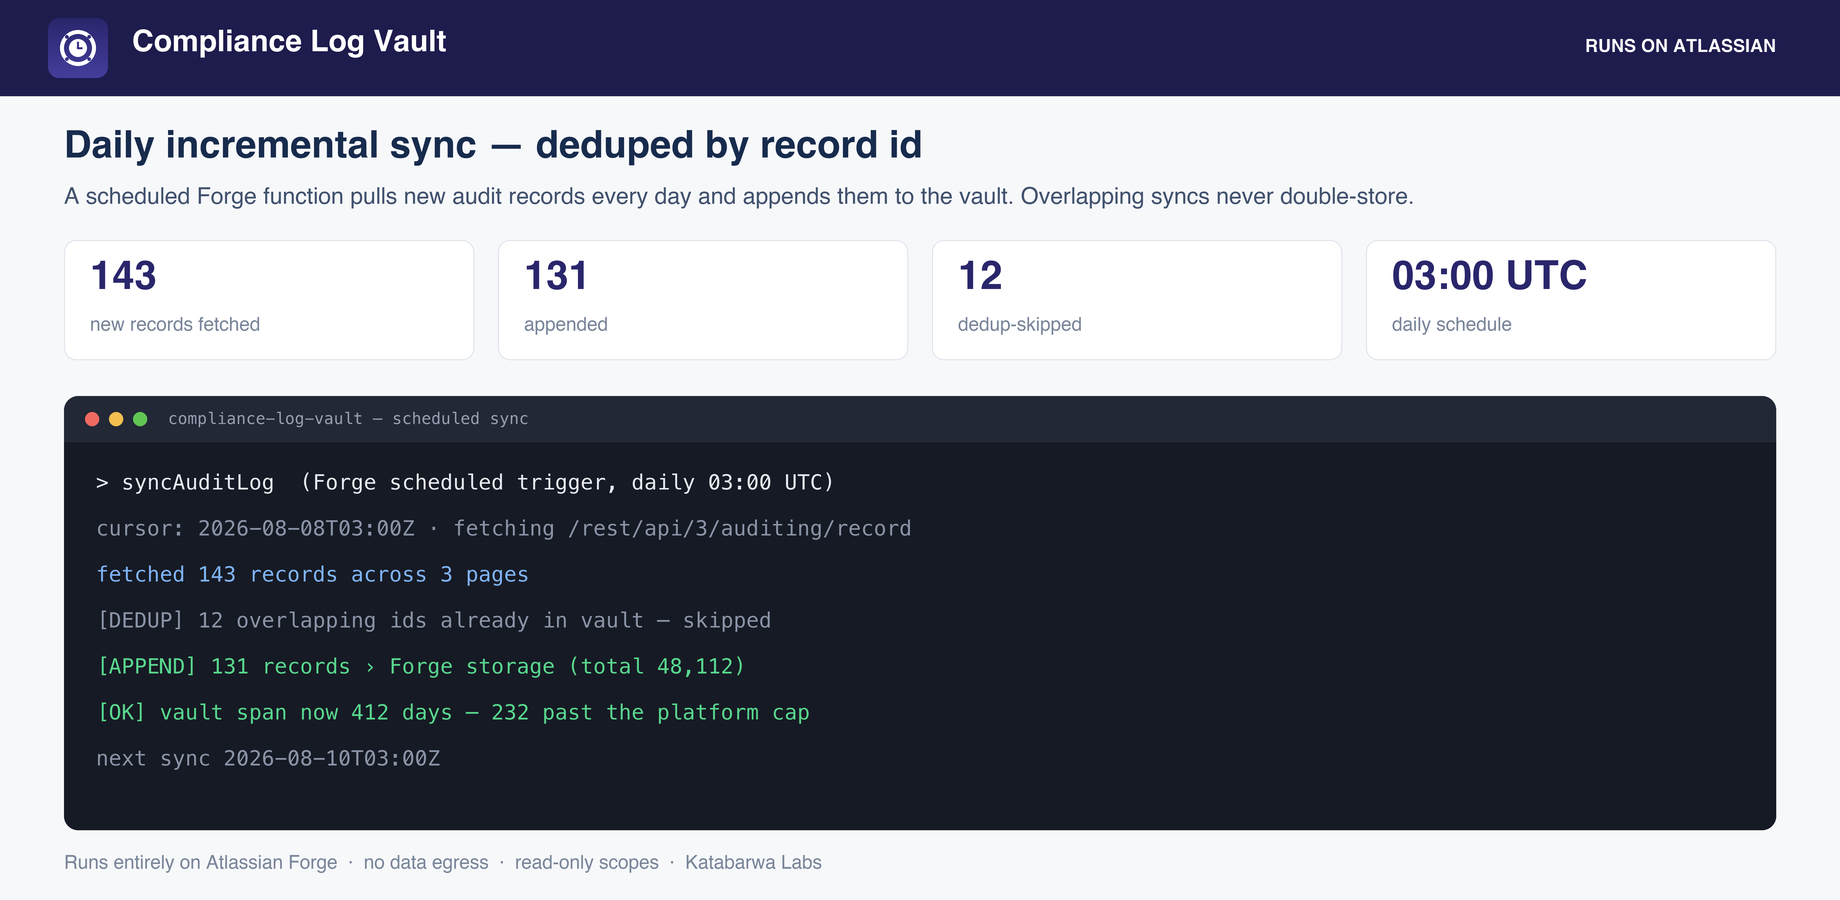
Runs entirely on Atlassian Forge inside your own tenant. No external servers, no data egress.
This app answers a request that has been open on Atlassian's public tracker for years: JRACLOUD-68267, "Jira audit log retention period needs to be increased", with 224 votes.
Jira's native audit log is capped: records older than roughly 180 days age out and are gone. When a SOC 2 or ISO auditor asks for last year's evidence, there is nothing to show. Raising the cap is one of the longest-standing open requests on the public tracker.
Built on Atlassian Forge: the app runs on Atlassian's own serverless platform inside your tenant, stores its data in Forge storage, and makes no external network calls. Every scope it requests, and why:
| read:audit-log:jira | reading the audit records |
| read:user:jira | required pair for the auditing endpoint |
| storage:app | the vault itself, in your tenant |
Atlassian's own documentation for what Jira does out of the box, so you can see exactly where the gap is:
No. The app runs on Atlassian Forge inside your own tenant with zero external egress, which makes it eligible for Atlassian's Runs on Atlassian trust marker.
Through the Atlassian Marketplace, on your existing Atlassian bill, priced per user like any Cloud app. The listing has a free evaluation and the exact calculator for your tier.
Email support@llmgraph.ai or open an issue from the documentation page. You talk directly to the people who build the app.
Free evaluation from the Marketplace listing. If it does not fit your workflow, tell us what would and we will build it.