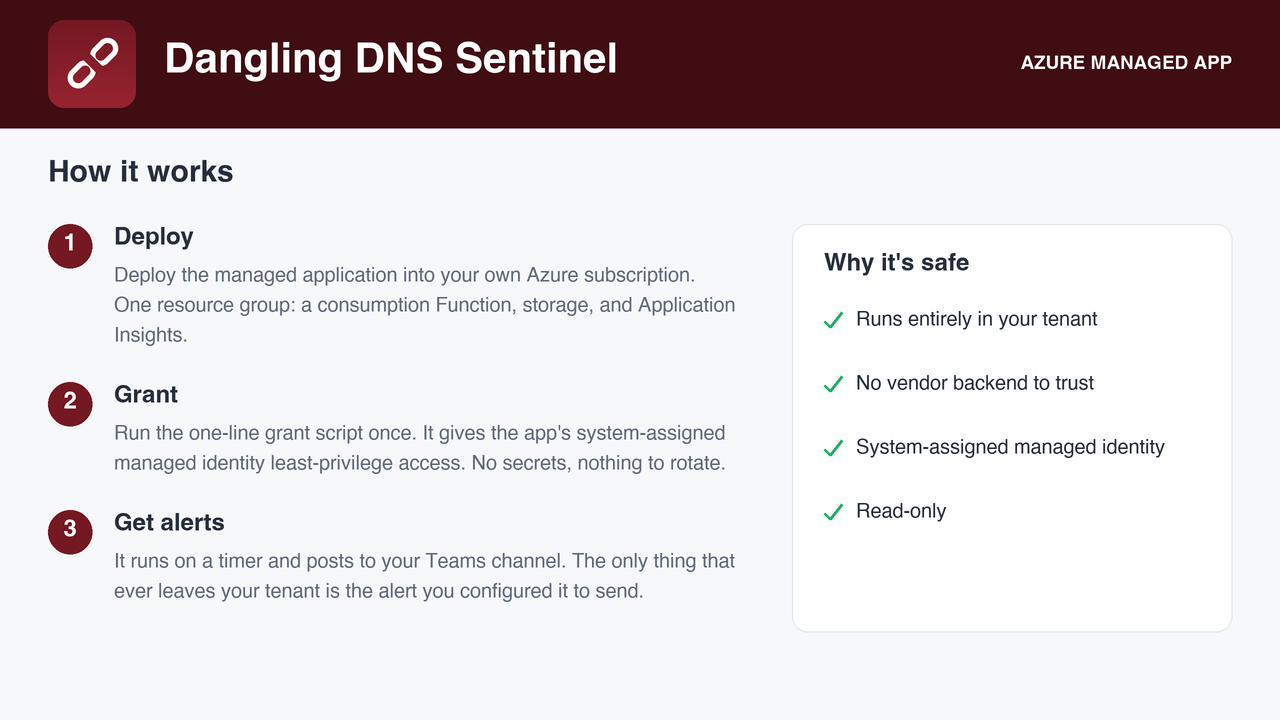
Deploys as a managed application in your own subscription. No vendor backend, no data egress.
Flat monthly fee, billed by Microsoft.
The gap
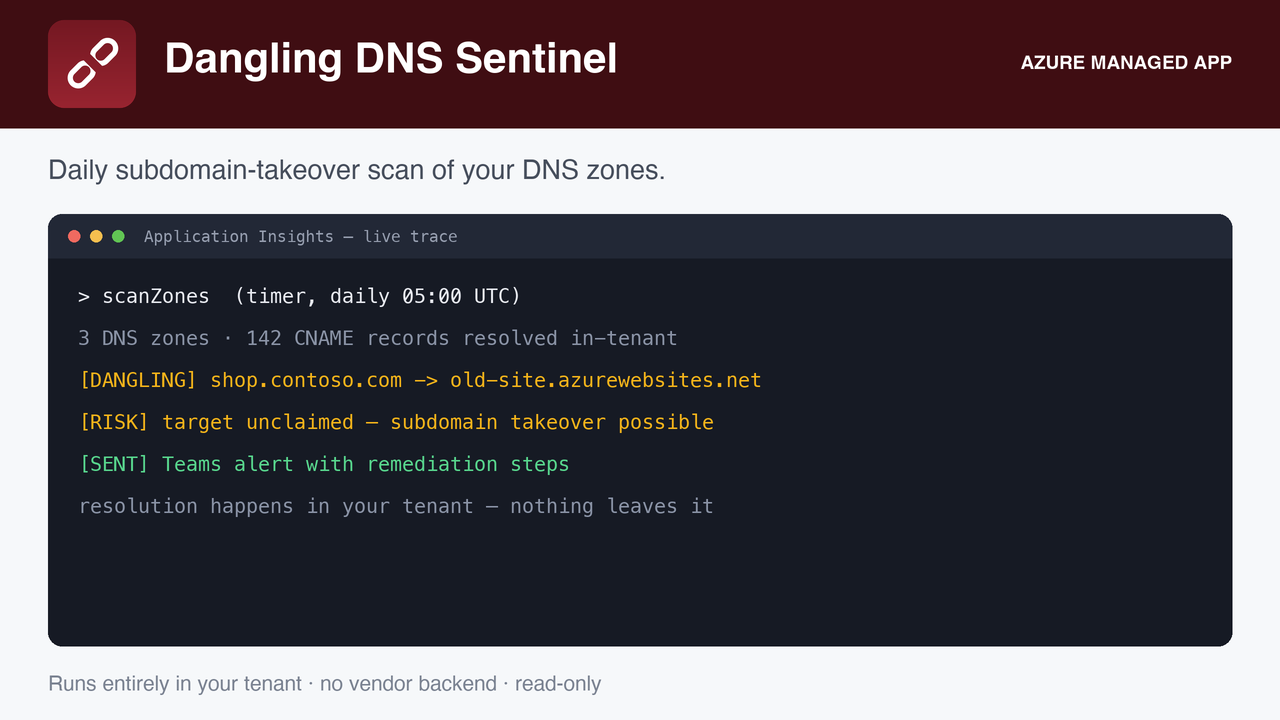
Microsoft documents the risk and provides Get-DanglingDnsRecords, a PowerShell script you run once. Resources are deleted every week. The gap between those two facts is where subdomain takeovers happen.
What it does
Enumerates every CNAME across all Azure DNS zones in the subscription daily.
Resolves each Azure-service target from inside your tenant and classifies it: dangling, review, unchecked, or ok.
Review covers Front Door, CDN, and Traffic Manager endpoints that resolve through wildcard DNS but whose backing resource cannot be confirmed as yours.
Records that fail to resolve this run are reported as unchecked, never counted as healthy.
Healthy records are not re-flagged daily, to avoid alert fatigue.
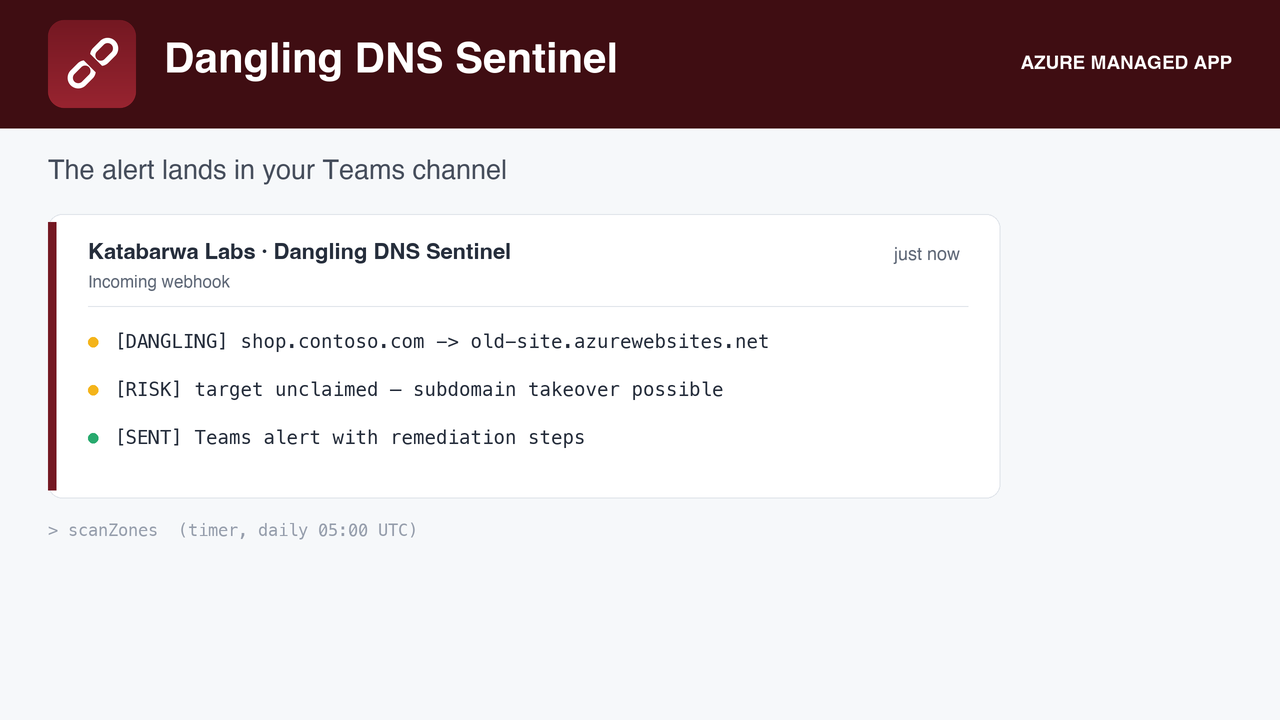
The daily report: dangling and review records with the target that no longer resolves.Zone-by-zone coverage.Classification detail for one record.
Honest about its limits
Read-only. It never changes DNS; removing or re-pointing a record is yours to do.
It covers Azure DNS zones. Zones hosted elsewhere are out of its view.
Read-only. This app reports and alerts; it changes nothing in your subscription.
How it runs, and what it needs
A serverless function on a schedule, with a system-assigned managed identity, deployed into your subscription
by the Azure Marketplace. Roles are granted by you after deployment with the one-line script in the package, so
nothing runs until you say so. Every role it asks for, and why:
Reader
list DNS zones and records
Alerts go to the Teams Workflows webhook you configure. Nothing is sent anywhere else.
FAQ
Does any data leave my subscription?
No. The function runs in your subscription and writes only to your configured alert destination. Katabarwa Labs operates no backend and receives nothing.
How is it billed?
A flat monthly fee on your Azure bill through the Marketplace, plus the small consumption cost of the function itself. No per-resource or per-user pricing.
How do I remove it?
Delete the managed application from the Azure portal. Its resource group and identity go with it, and any role you granted can be removed the same way.