One digest of every expiring Key Vault secret, key, and certificate
Key Vault notifications are per vault, fire once, and ignore objects with no expiry date. This is one daily digest across every vault in the subscription.
Deploys as a managed application in your own subscription. No vendor backend, no data egress.
Flat monthly fee, billed by Microsoft.
The gap
Each vault can notify once, through Event Grid, if someone wired it up. There is no recurring reminder, no view across vaults, and nothing at all about the secrets that never expire because nobody set a date. Those are the ones that get forgotten.
What it does
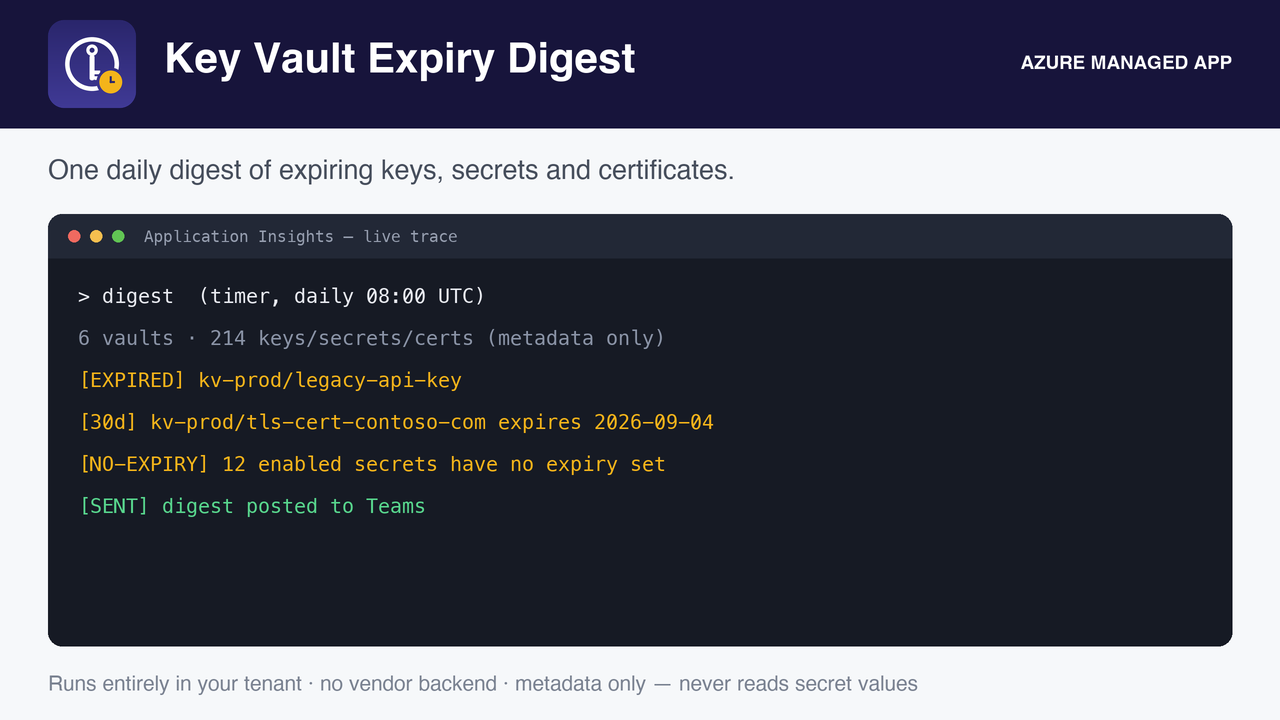
Enumerates every Key Vault in the subscription and every key, secret, and certificate in them.
Reports expired objects, objects expiring within your thresholds, and enabled objects with no expiry set.
Re-reports daily until each object is renewed or given an expiry, so nothing lapses quietly.
Reads object metadata only, names and dates, through the management plane. It can never read secret values or key material.
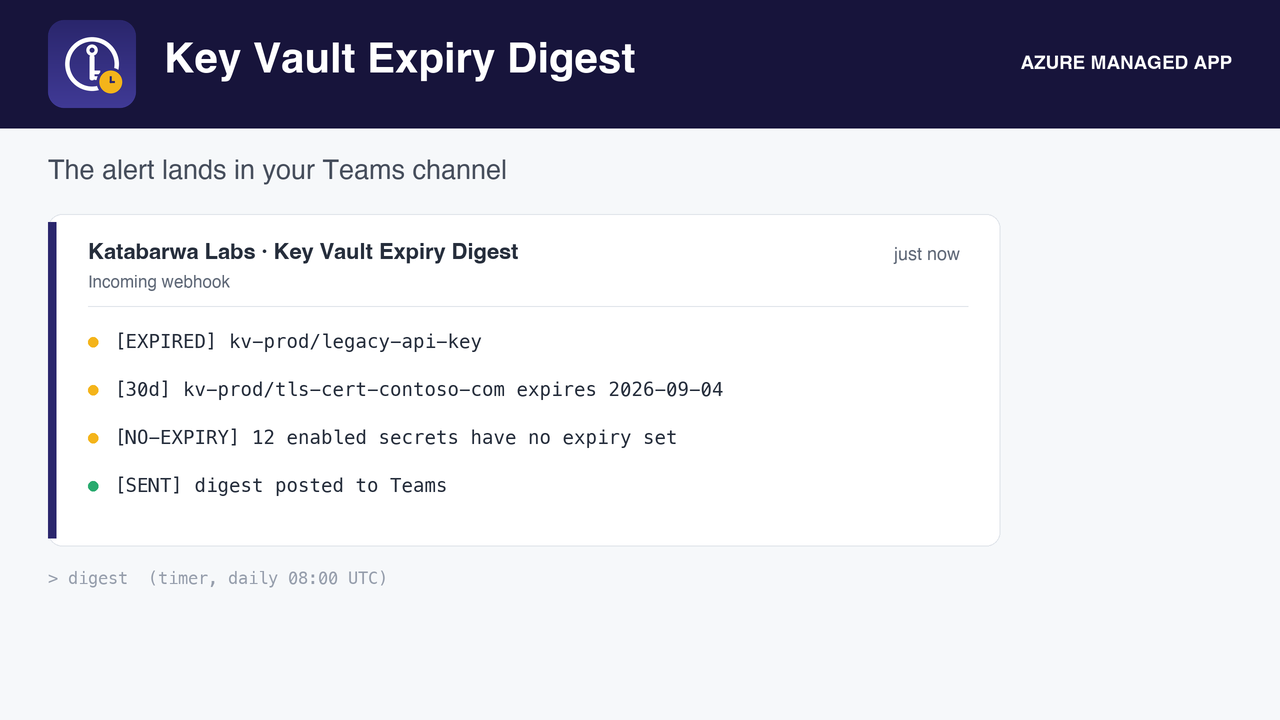
One Adaptive Card to Teams per day, worst first.
The digest: expired, expiring, and never-expiring objects across all vaults.Per-object rows with vault, type, and days remaining.Scan history in your own Application Insights.
Honest about its limits
It reports; it does not rotate or set expiry dates for you.
Vaults the identity cannot read are listed as unreadable rather than silently skipped.
Read-only. This app reports and alerts; it changes nothing in your subscription.
How it runs, and what it needs
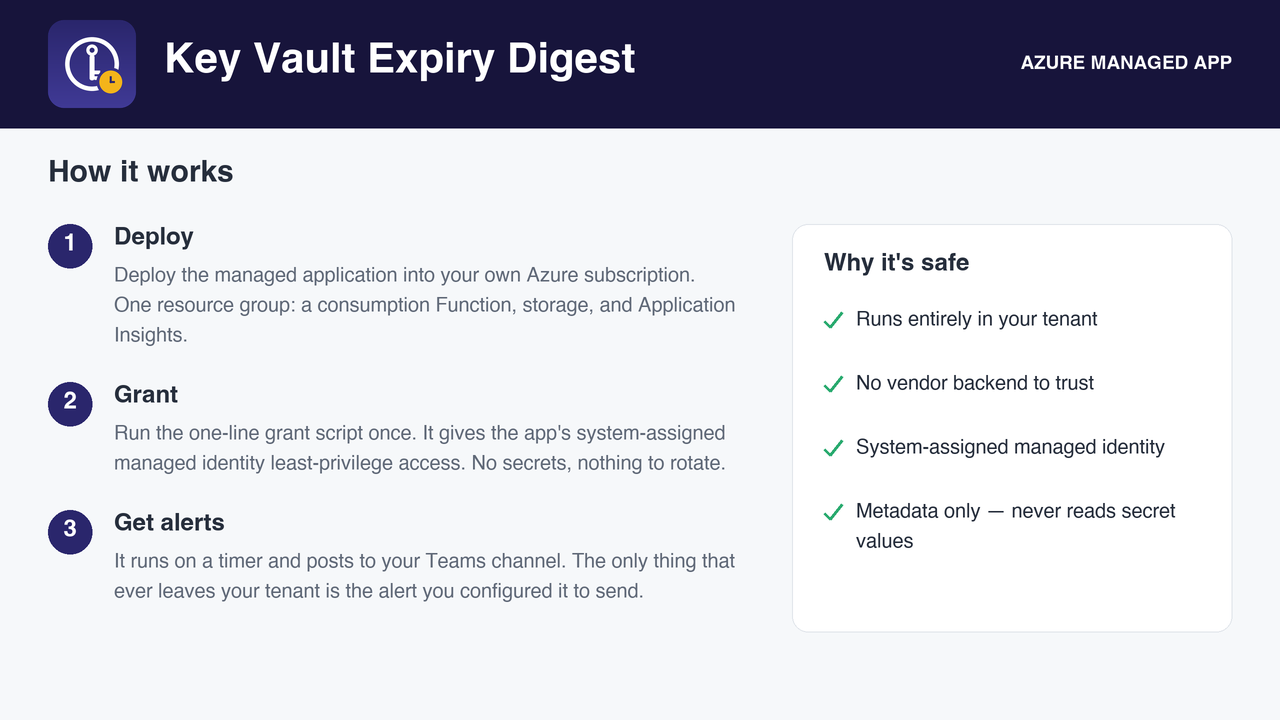
A serverless function on a schedule, with a system-assigned managed identity, deployed into your subscription
by the Azure Marketplace. Roles are granted by you after deployment with the one-line script in the package, so
nothing runs until you say so. Every role it asks for, and why:
Key Vault Reader
list vaults and read object metadata, never values
Alerts go to the Teams webhook you configure. Nothing is sent anywhere else.
FAQ
Does any data leave my subscription?
No. The function runs in your subscription and writes only to your configured alert destination. Katabarwa Labs operates no backend and receives nothing.
How is it billed?
A flat monthly fee on your Azure bill through the Marketplace, plus the small consumption cost of the function itself. No per-resource or per-user pricing.
How do I remove it?
Delete the managed application from the Azure portal. Its resource group and identity go with it, and any role you granted can be removed the same way.
Deploy Key Vault Expiry Digest in your subscription.
Key Vault notifications are per vault, fire once, and ignore objects with no expiry date. This is one daily digest across every vault in the subscription.