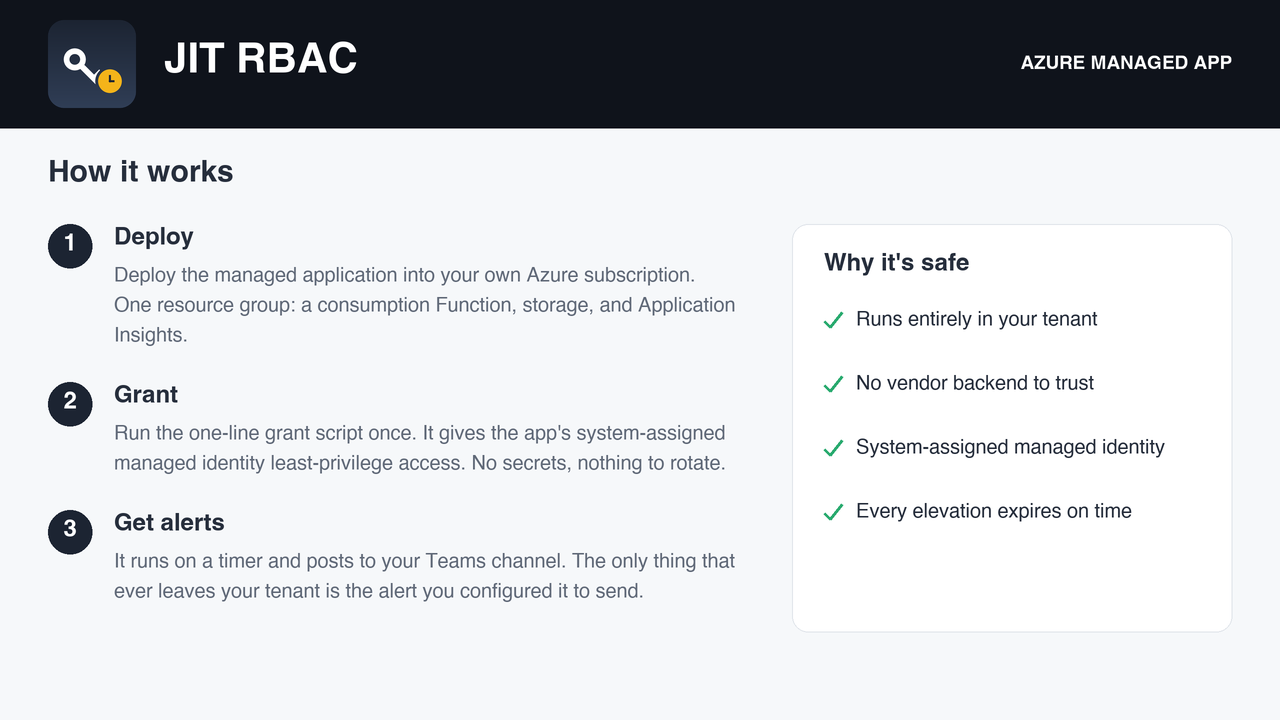
Deploys as a managed application in your own subscription. No vendor backend, no data egress.
Flat monthly fee, billed by Microsoft.
The gap
Standing Contributor and Owner assignments are how most Azure estates end up over-privileged, and the fix Microsoft sells, Privileged Identity Management, requires Entra P2 for every user. The day-to-day need is small: a few hours of a role, approved by someone, gone afterwards.
What it does
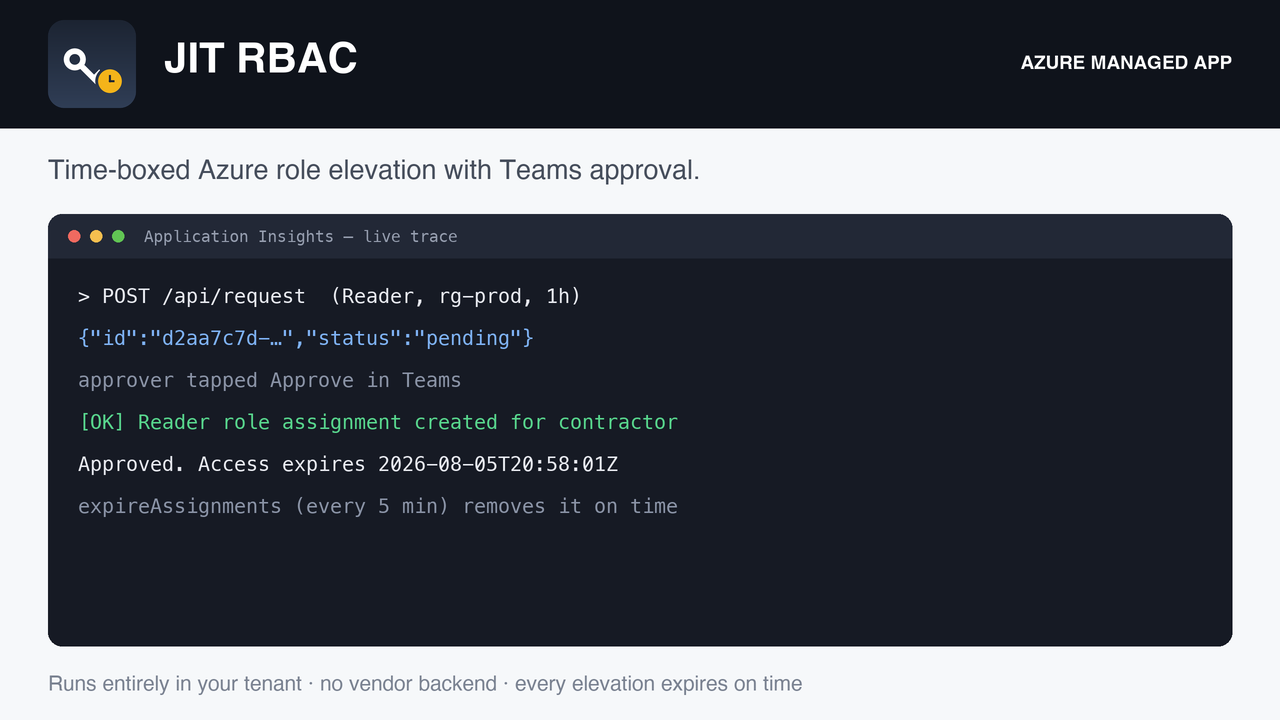
A request names the requester, role, scope, duration, and justification; an approval card lands in Teams.
Approve and Deny links are HMAC-signed, expire, and require an explicit confirmation click, so a link preview or scanner can never approve.
On approval the requester is resolved through Microsoft Graph and the role assignment is created at the requested ARM scope.
A five-minute timer removes each assignment when its duration elapses. That removal is the guarantee.
Every request, decision, and expiry is recorded in the app's own table storage for audit.
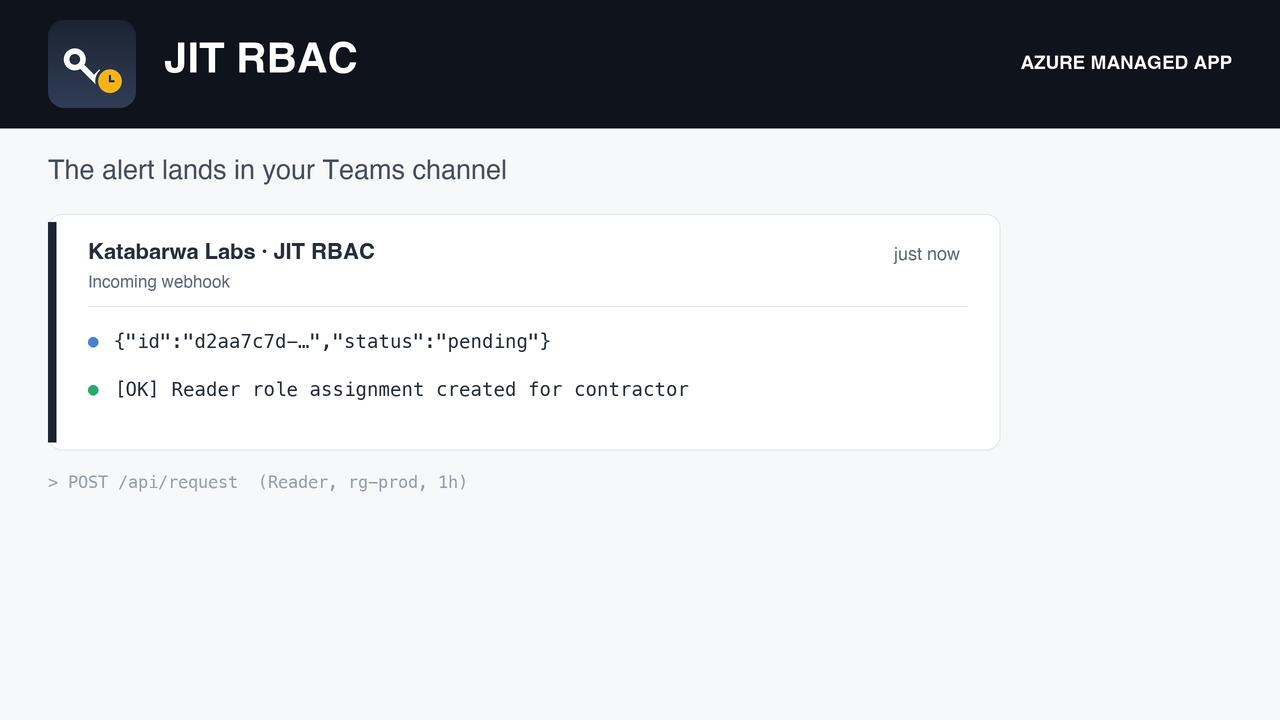
The approval card in Teams: who, which role, which scope, how long, and why.Active elevations with their expiry, and the audit trail behind them.Request flow from a Teams command or an internal page to the function.
Honest about its limits
It manages Azure resource RBAC at subscription, resource group, and resource scope. It does not manage Entra directory roles such as Global Administrator; those need the PIM API and P2.
The requesting surface is an HTTP endpoint you wire to Teams, a Logic App, or a page; a chat bot is not included.
The one write path, honestly scoped: Creating a role assignment on approval and removing it when the window ends. Nothing else is written.
How it runs, and what it needs
A serverless function on a schedule, with a system-assigned managed identity, deployed into your subscription
by the Azure Marketplace. Roles are granted by you after deployment with the one-line script in the package, so
nothing runs until you say so. Every role it asks for, and why:
User Access Administrator
create and remove role assignments at the scopes JIT manages
Microsoft Graph User.Read.All
resolve requesters to real people and reject unknown principals
Alerts go to the Teams channel behind your Workflows webhook. Nothing is sent anywhere else.
FAQ
Does any data leave my subscription?
No. The function runs in your subscription and writes only to your configured alert destination. Katabarwa Labs operates no backend and receives nothing.
How is it billed?
A flat monthly fee on your Azure bill through the Marketplace, plus the small consumption cost of the function itself. No per-resource or per-user pricing.
How do I remove it?
Delete the managed application from the Azure portal. Its resource group and identity go with it, and any role you granted can be removed the same way.