This app answers a request that has been open on Atlassian's public tracker for years:
JRACLOUD-71967,
"Group usage: list of project permissions per group", with 1,002 votes.
We wrote up the problem and the native workarounds on Atlassian Community.
The gap
Jira has no screen that answers "which projects can this user reach, and why?" or "where is this group actually used?" Permission schemes, project roles, and group memberships each tell a fragment; the effective answer lives in nobody's head. Access reviews end up as spreadsheets built from a dozen admin screens.
What it does
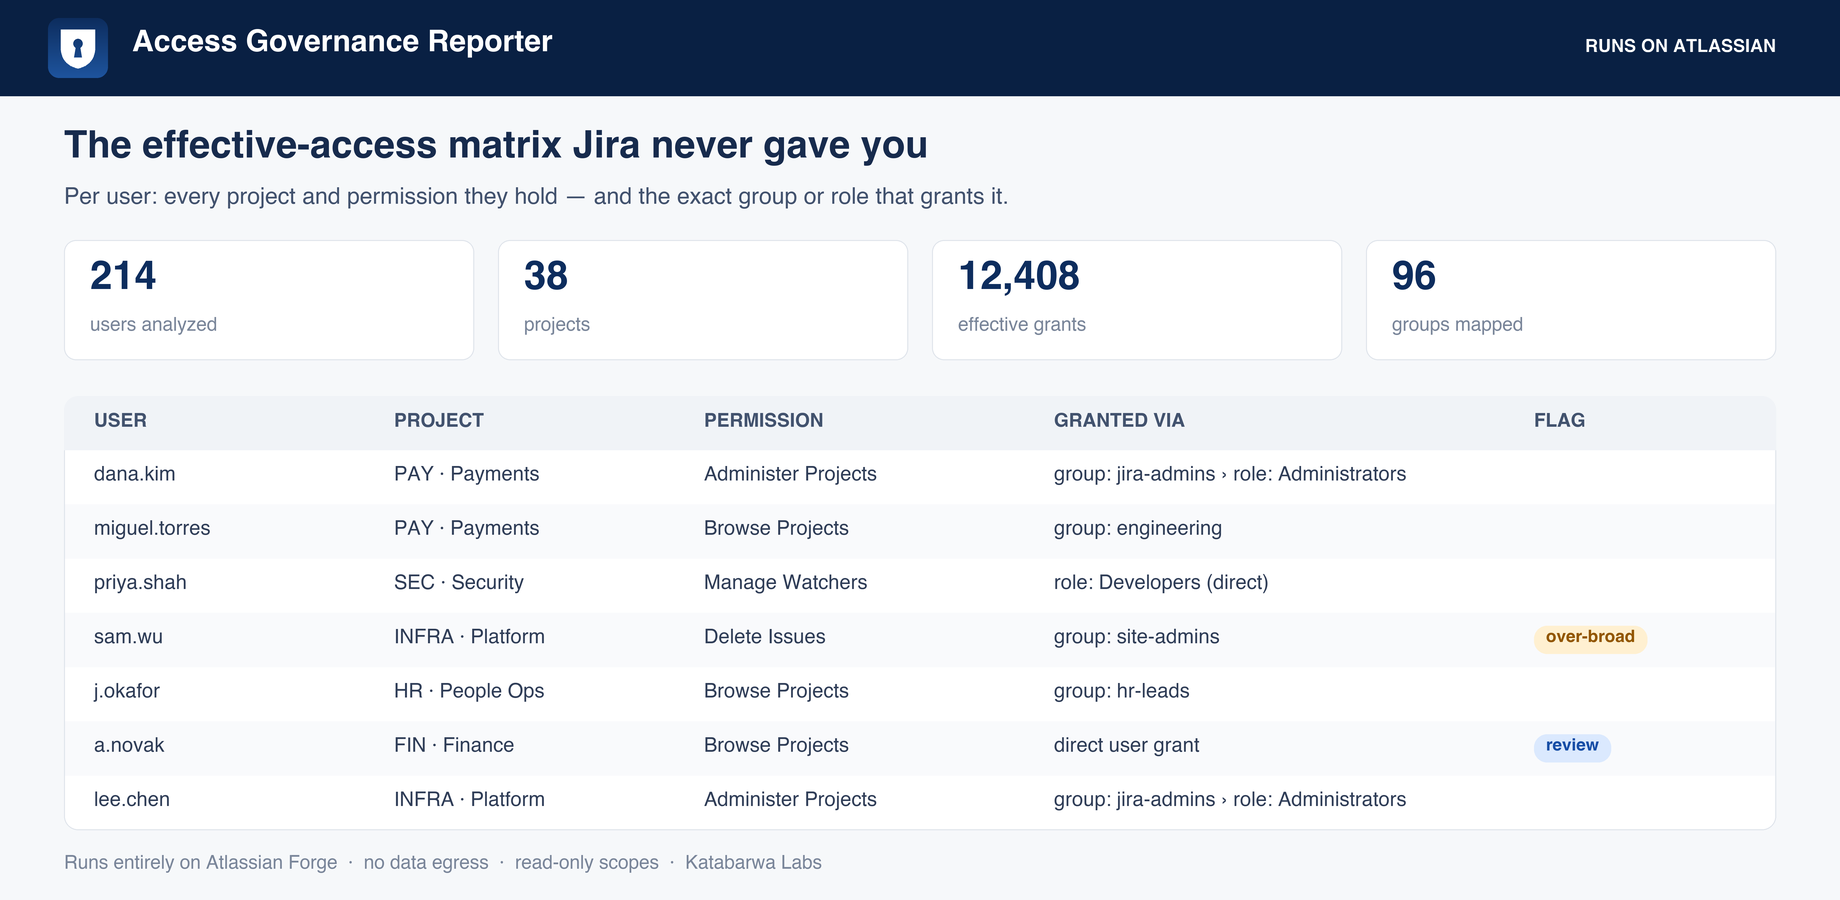
Effective-access matrix: per user, which projects and permissions, via which group or role path.
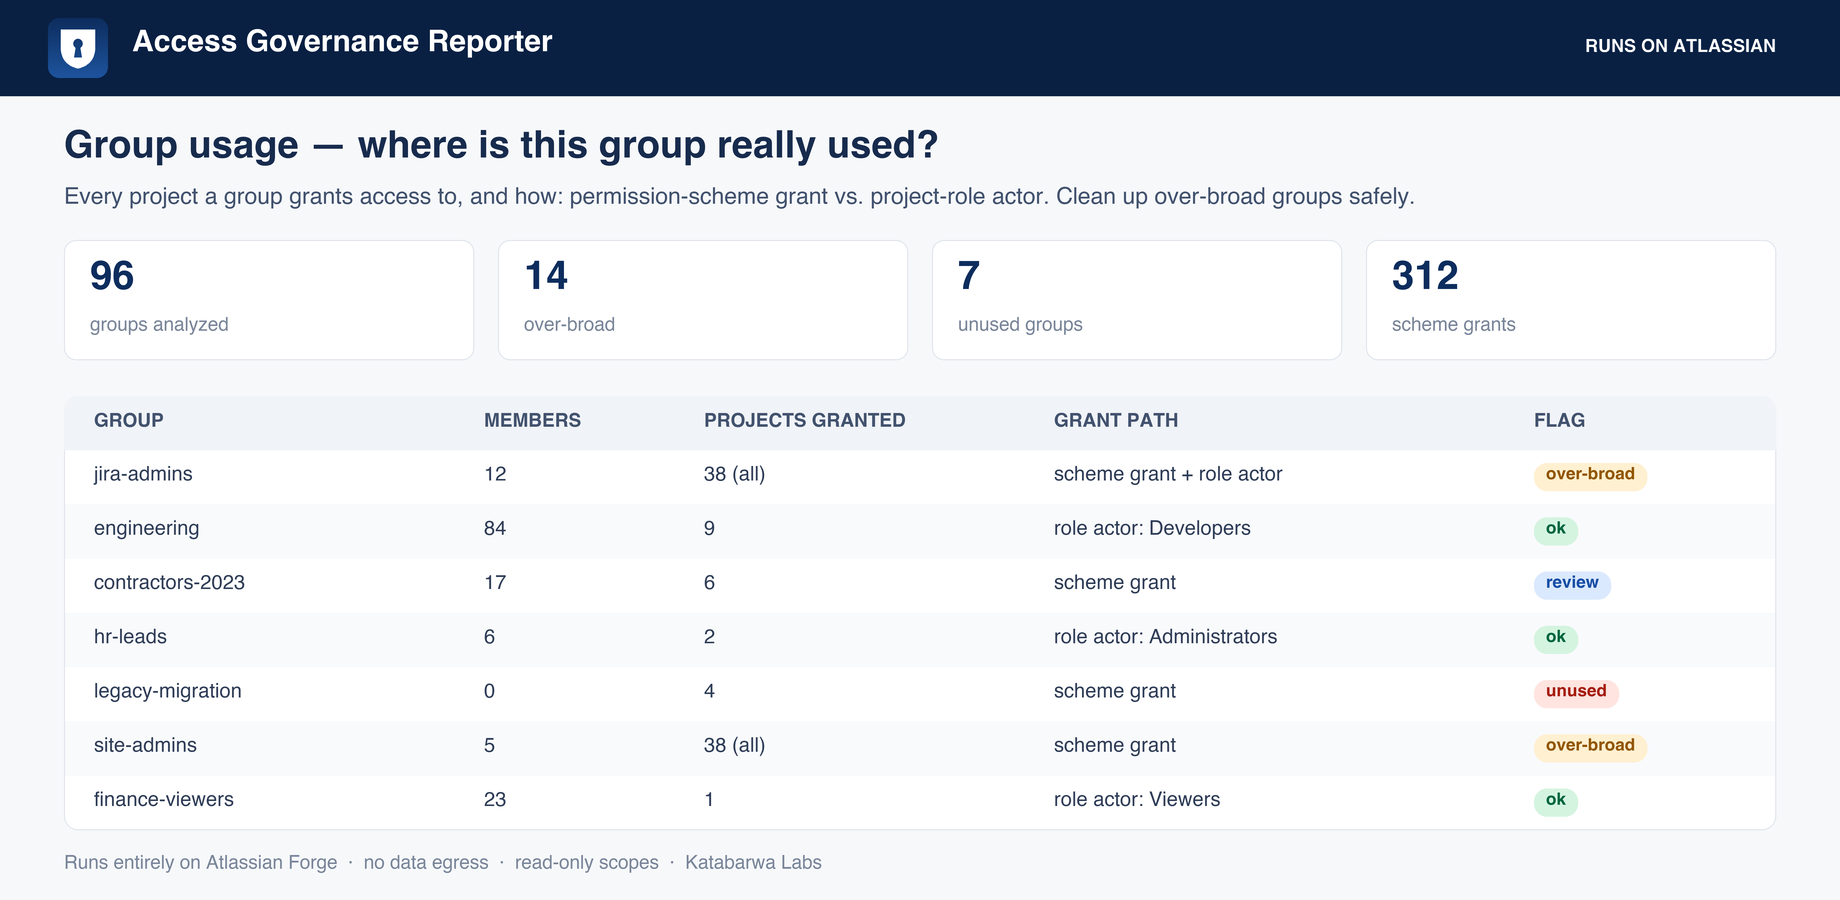
Group-usage view: every project a group grants access to, and how (scheme grant vs project role).
Handles group membership, project-role actors (users and group actors), and direct user grants.
Summary-first report: instant dashboard at any site size, detail pages in on demand with server-side search.
Daily automatic refresh, cached in-tenant for instant reporting.
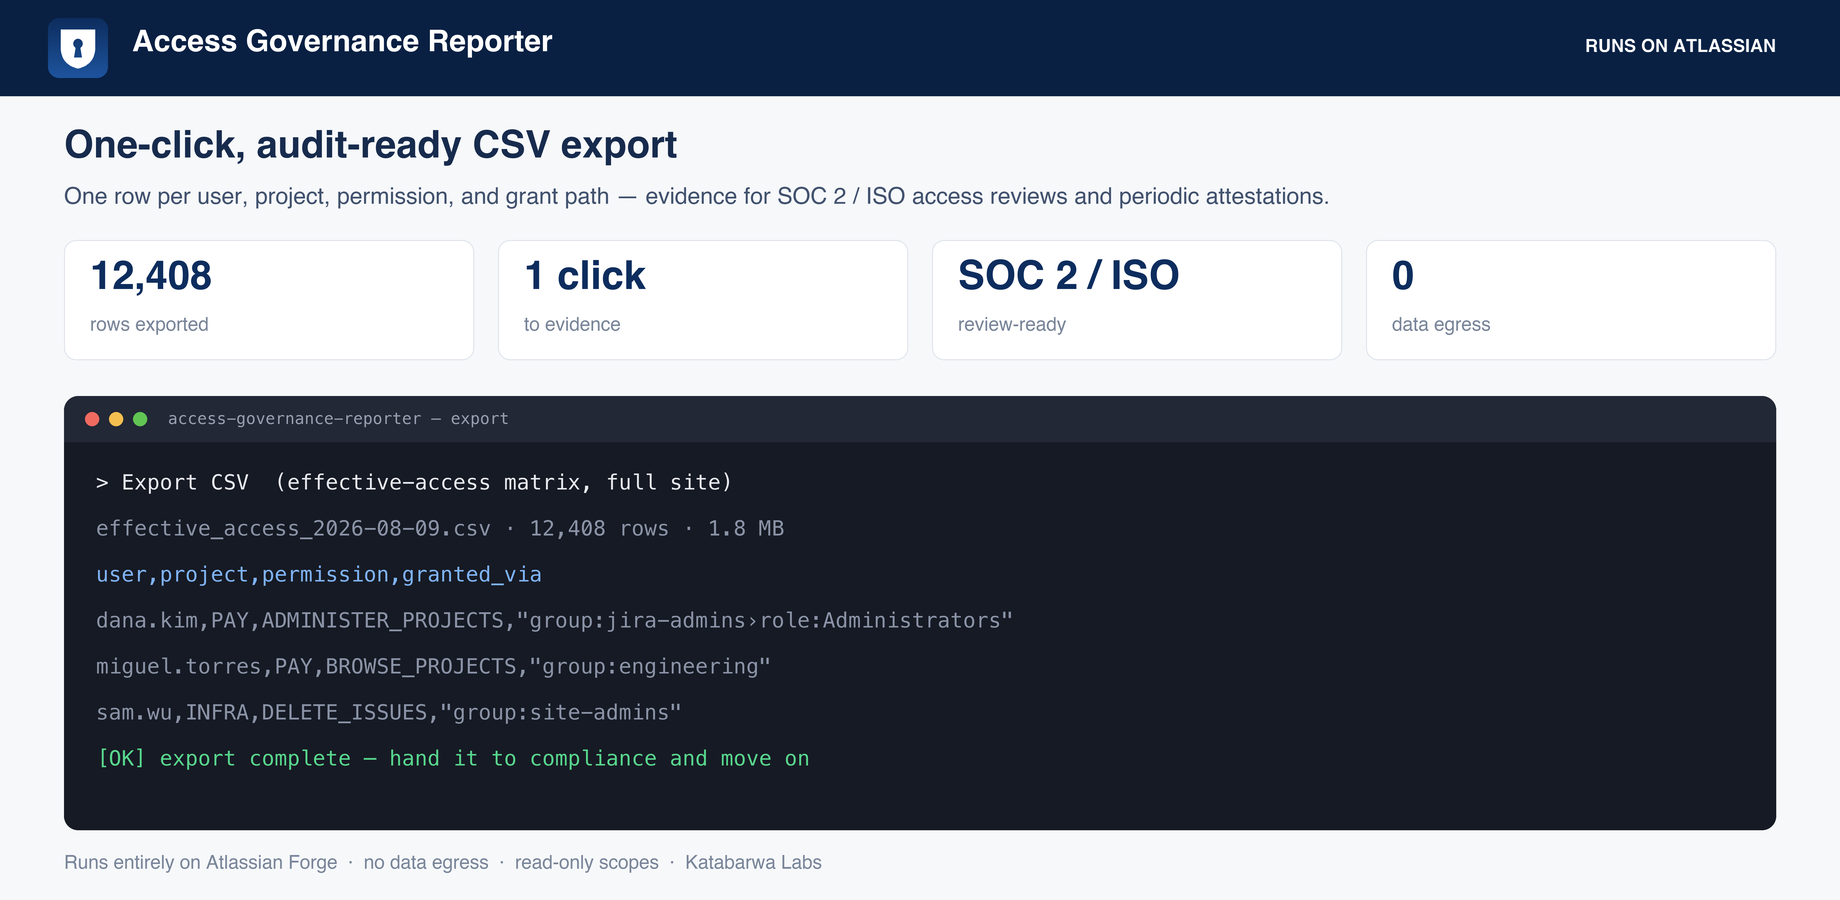
One-click CSV attestation export, one row per grant path.
The effective-access matrix: every user, every project, every permission, and the grant path behind it.Group usage in both directions: what a group grants, and what a user holds through it.The daily crawl streams per-project facts into bounded, paged storage.
Honest about its limits
Global-permission grantees cannot be enumerated through any public Jira Cloud API, so that surface is reported as not coverable rather than silently omitted.
The report reflects the last completed crawl; changes made minutes ago appear after the next refresh or a manual rescan.
The one write path, honestly scoped: An opt-in, preview-first revocation can remove deactivated users from groups and roles. It is dry-run by default, shows the exact change set, requires explicit confirmation, re-checks that each account is still deactivated before acting, and removes access only. It never deactivates accounts.
Security & permissions
Built on Atlassian Forge: the app runs on Atlassian's own serverless platform inside your
tenant, stores its data in Forge storage, and makes no external network calls. Every scope it
requests, and why:
read:jira-work
projects, permission schemes, and project roles
read:jira-user
user details for the matrix and CSV
storage:app
the cached report, entirely in your tenant
The native feature it builds on
Atlassian's own documentation for what Jira does out of the box, so you can see exactly where the gap is:
No. The app runs on Atlassian Forge inside your own tenant with zero external egress,
which makes it eligible for Atlassian's Runs on Atlassian trust marker.
How is it billed?
Through the Atlassian Marketplace, on your existing Atlassian bill, priced per user like
any Cloud app. The listing has a free evaluation and the exact calculator for your tier.