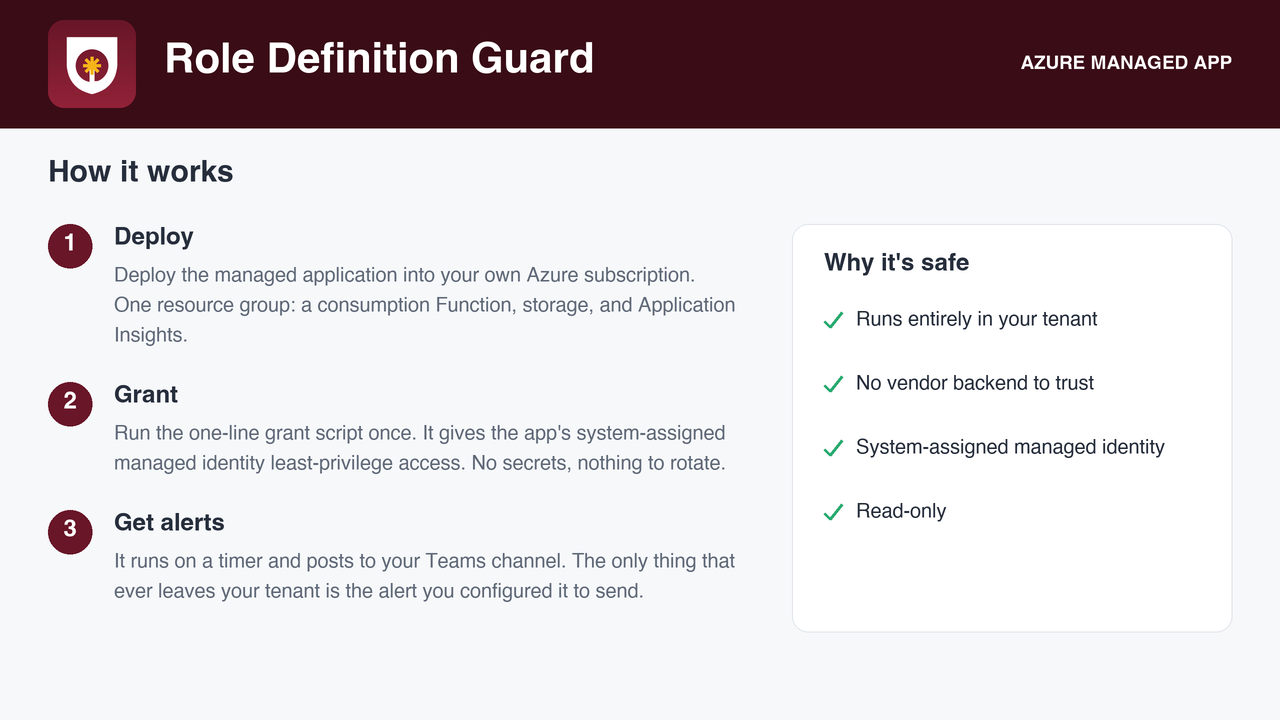
Deploys as a managed application in your own subscription. No vendor backend, no data egress.
Flat monthly fee, billed by Microsoft.
The gap
A custom role named "App Deployer" that grants Microsoft.Authorization/* hands its holders the ability to give themselves anything. The built-in policy that used to catch this is deprecated, and Defender for Cloud looks at who is Owner, not at what your custom roles actually permit.
What it does
Weekly scan of every custom role definition at the configured scope through the management plane, including who changed it and when.
Wildcard-aware matching with notActions subtraction, so a capability is only reported when it is effectively granted.
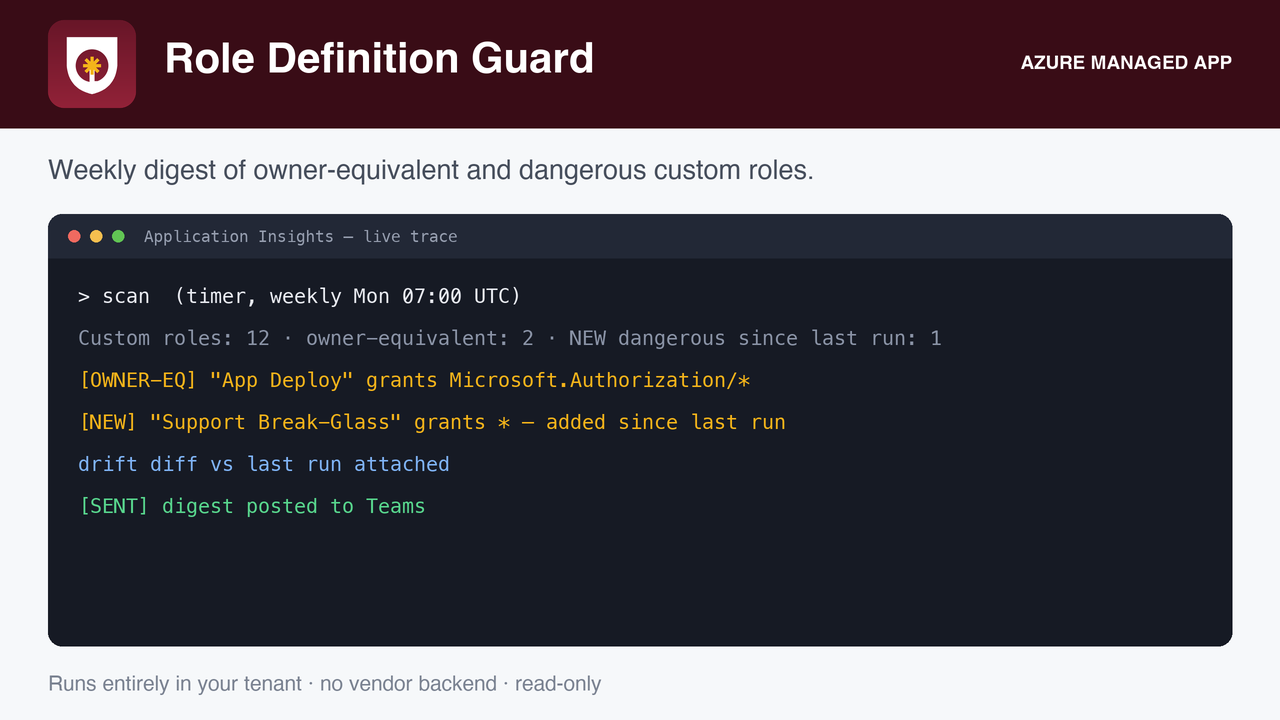
Flags dangerous patterns: bare *, Microsoft.Authorization/*, role and deny assignment writes, elevateAccess, and service-level wildcards.
An owner-equivalent verdict for roles that can actually grant or modify access, distinct from merely broad roles.
Drift: new dangerous roles and roles whose dangerous permission set grew are called out against last week's snapshot.
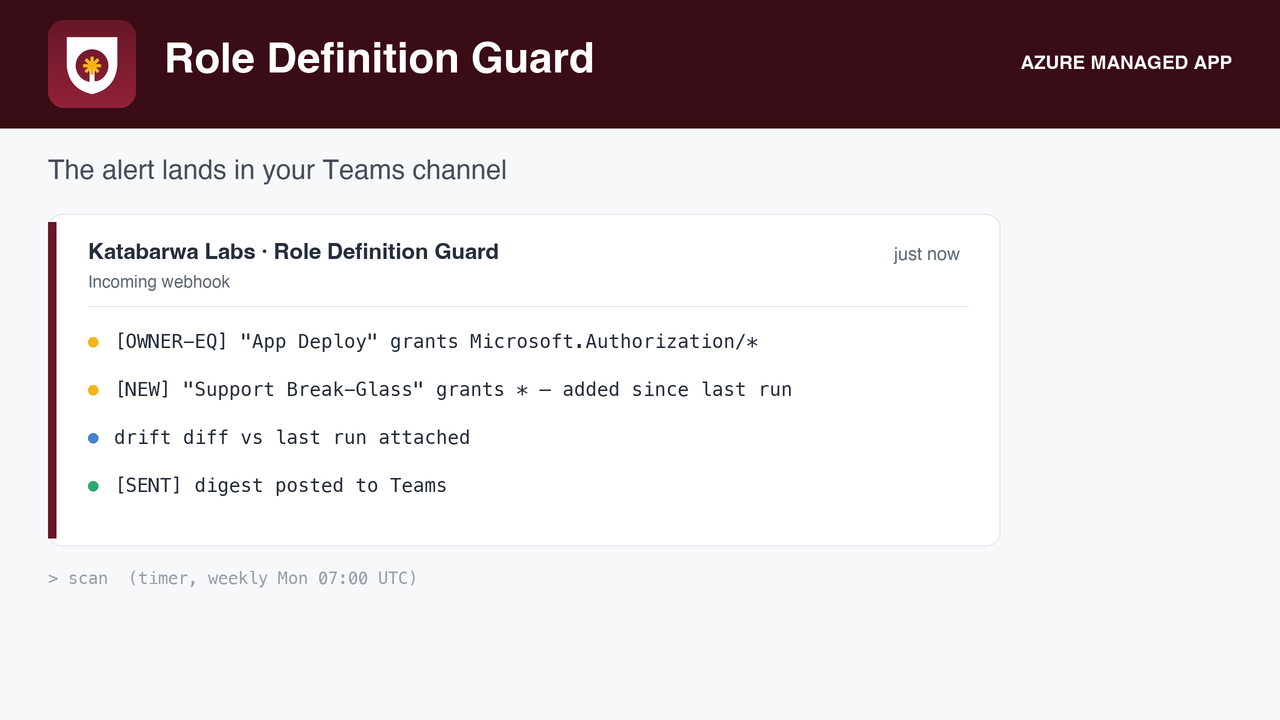
The weekly digest: each dangerous custom role, why it is dangerous, and whether it can grant access.Drift since last run: new roles and roles that grew.The permission analysis, with notActions carve-outs applied.
Honest about its limits
Read-only by design. It reports; it never edits or deletes a role definition.
"Last changed by" is shown as a principal object id, because resolving it to a name would need a Graph permission we chose not to request to keep the identity Reader-only.
Read-only. This app reports and alerts; it changes nothing in your subscription.
How it runs, and what it needs
A serverless function on a schedule, with a system-assigned managed identity, deployed into your subscription
by the Azure Marketplace. Roles are granted by you after deployment with the one-line script in the package, so
nothing runs until you say so. Every role it asks for, and why:
Reader
list custom role definitions and their permissions at the scanned scope
Alerts go to the Teams webhook you configure. Nothing is sent anywhere else.
FAQ
Does any data leave my subscription?
No. The function runs in your subscription and writes only to your configured alert destination. Katabarwa Labs operates no backend and receives nothing.
How is it billed?
A flat monthly fee on your Azure bill through the Marketplace, plus the small consumption cost of the function itself. No per-resource or per-user pricing.
How do I remove it?
Delete the managed application from the Azure portal. Its resource group and identity go with it, and any role you granted can be removed the same way.